In Kazakhstan, the protection of personal data in government systems has been strengthened.
Now, when working with databases containing more than 100,000 records of restricted personal data, multi-factor authentication, including biometric authentication, is mandatory. This measure is aimed at accurate user identification and reducing the risk of unauthorized access to personal data.
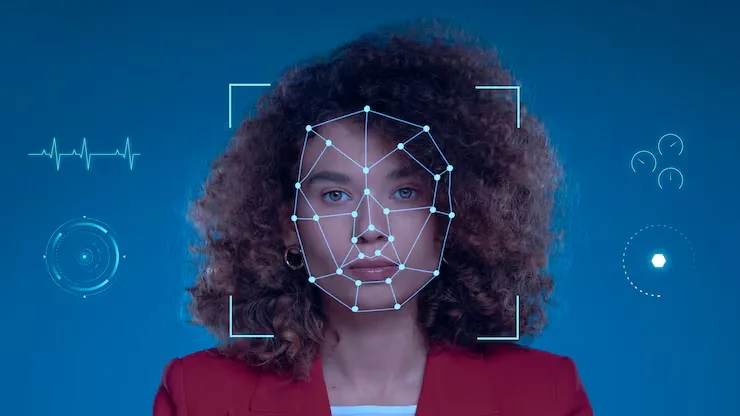
The Committee on Information Security of the Ministry of Artificial Intelligence and Digital Development of the Republic of Kazakhstan announces the entry into force of updated rules on personal data protection, aimed at strengthening the information security of state digital systems and protecting citizens' data.
As of December 22, 2025, amendments to the Rules on Implementing Measures to Protect Personal Data have entered into force. The new provisions strengthen access control to restricted data, particularly for large databases containing more than 100,000 records.
Now, owners, operators, and third parties working with such large volumes of personal data are required to use multi-factor authentication, including biometric methods. This will significantly reduce the risk of unauthorized access and enhance the security of digital systems.
Doszhan Musaliyev, Vice Minister
Additionally, the methodologies and rules for conducting tests of "e-government" informatization objects and critical information and communication infrastructure facilities for compliance with information security requirements have been updated. The new norms establish a three-year validity period for test protocols, after which re-testing is required.
The adopted changes are part of the state's systematic efforts to strengthen cybersecurity, protect citizens' personal data, and ensure the stable operation of digital services amid growing volumes of information and increasing cyber threat risks.
Source: Gov.kz
The Tech on Telegram Follow The Tech on Telegram
Keep up with the latest technology and startup news.
Related reading
More from this author

Article Useful
How to protect your accounts from hacking: 8 settings you should check today
The Tech

Article Useful
500 Global: How the Accelerator Works and Who Can Receive Investments
The Tech

Article Interviews
Game Development in Central Asia: Arkady Moldavski on Developing Reverb and the Growth of the Industry
The Tech

Article Useful
Google, Tesla, BlackRock, and the IMF: Where to Apply for an Internship in Fall 2026
The Tech

News IT
Tesla unveiled the flying electric car Roadster
The Tech

News IT
Intero Biosystems startup won the Startup Battlefield at TechCrunch Disrupt 2026
The Tech