Information Security in a Startup: From Mistakes to Resilience
Author - Mansur Ismagulov
The Tech AI
Get the key points in seconds - a short summary from The Tech AI.
Venture investor Alim Khamitov and expert Evgeny Pitolin discussed startups' neglect of cybersecurity. Founders often delay data protection, leading to data breaches and fines for violating personal data laws. The speakers recommend engaging external experts, implementing Bug Bounty programs, and fostering a security culture from day one.
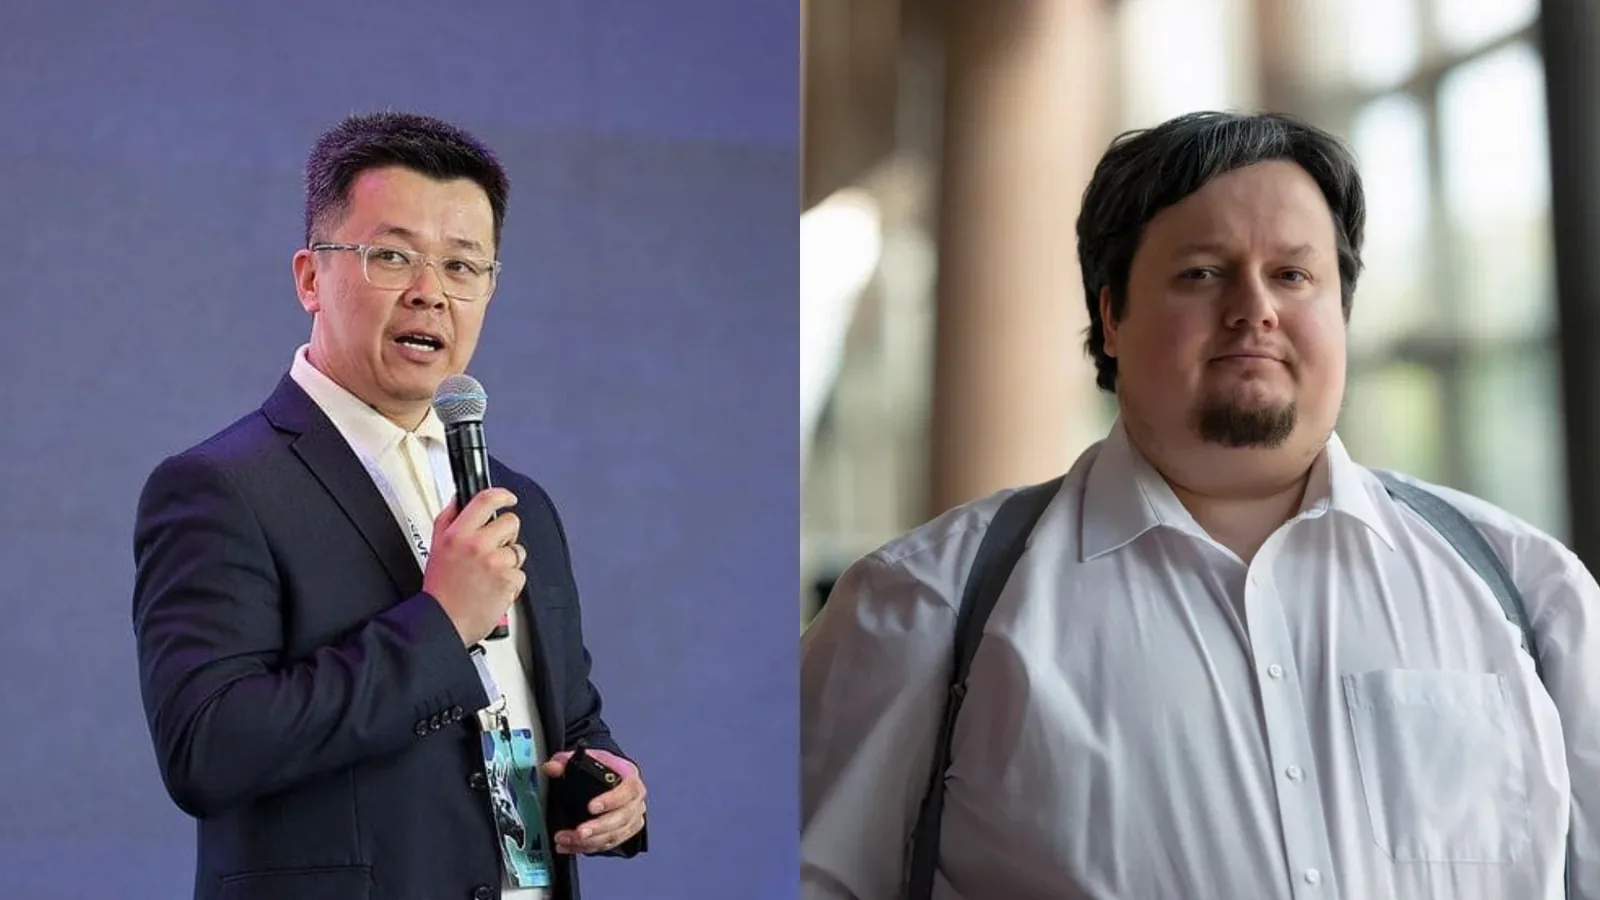
Recently, a live stream took place in the Telegram channel The Tech, featuring venture capitalist Alim Khamitov and cybersecurity expert Evgeny Pitolin. The speakers discussed why startups ignore data protection, common founder mistakes, when to bring in advisors, and how to build an information security culture.
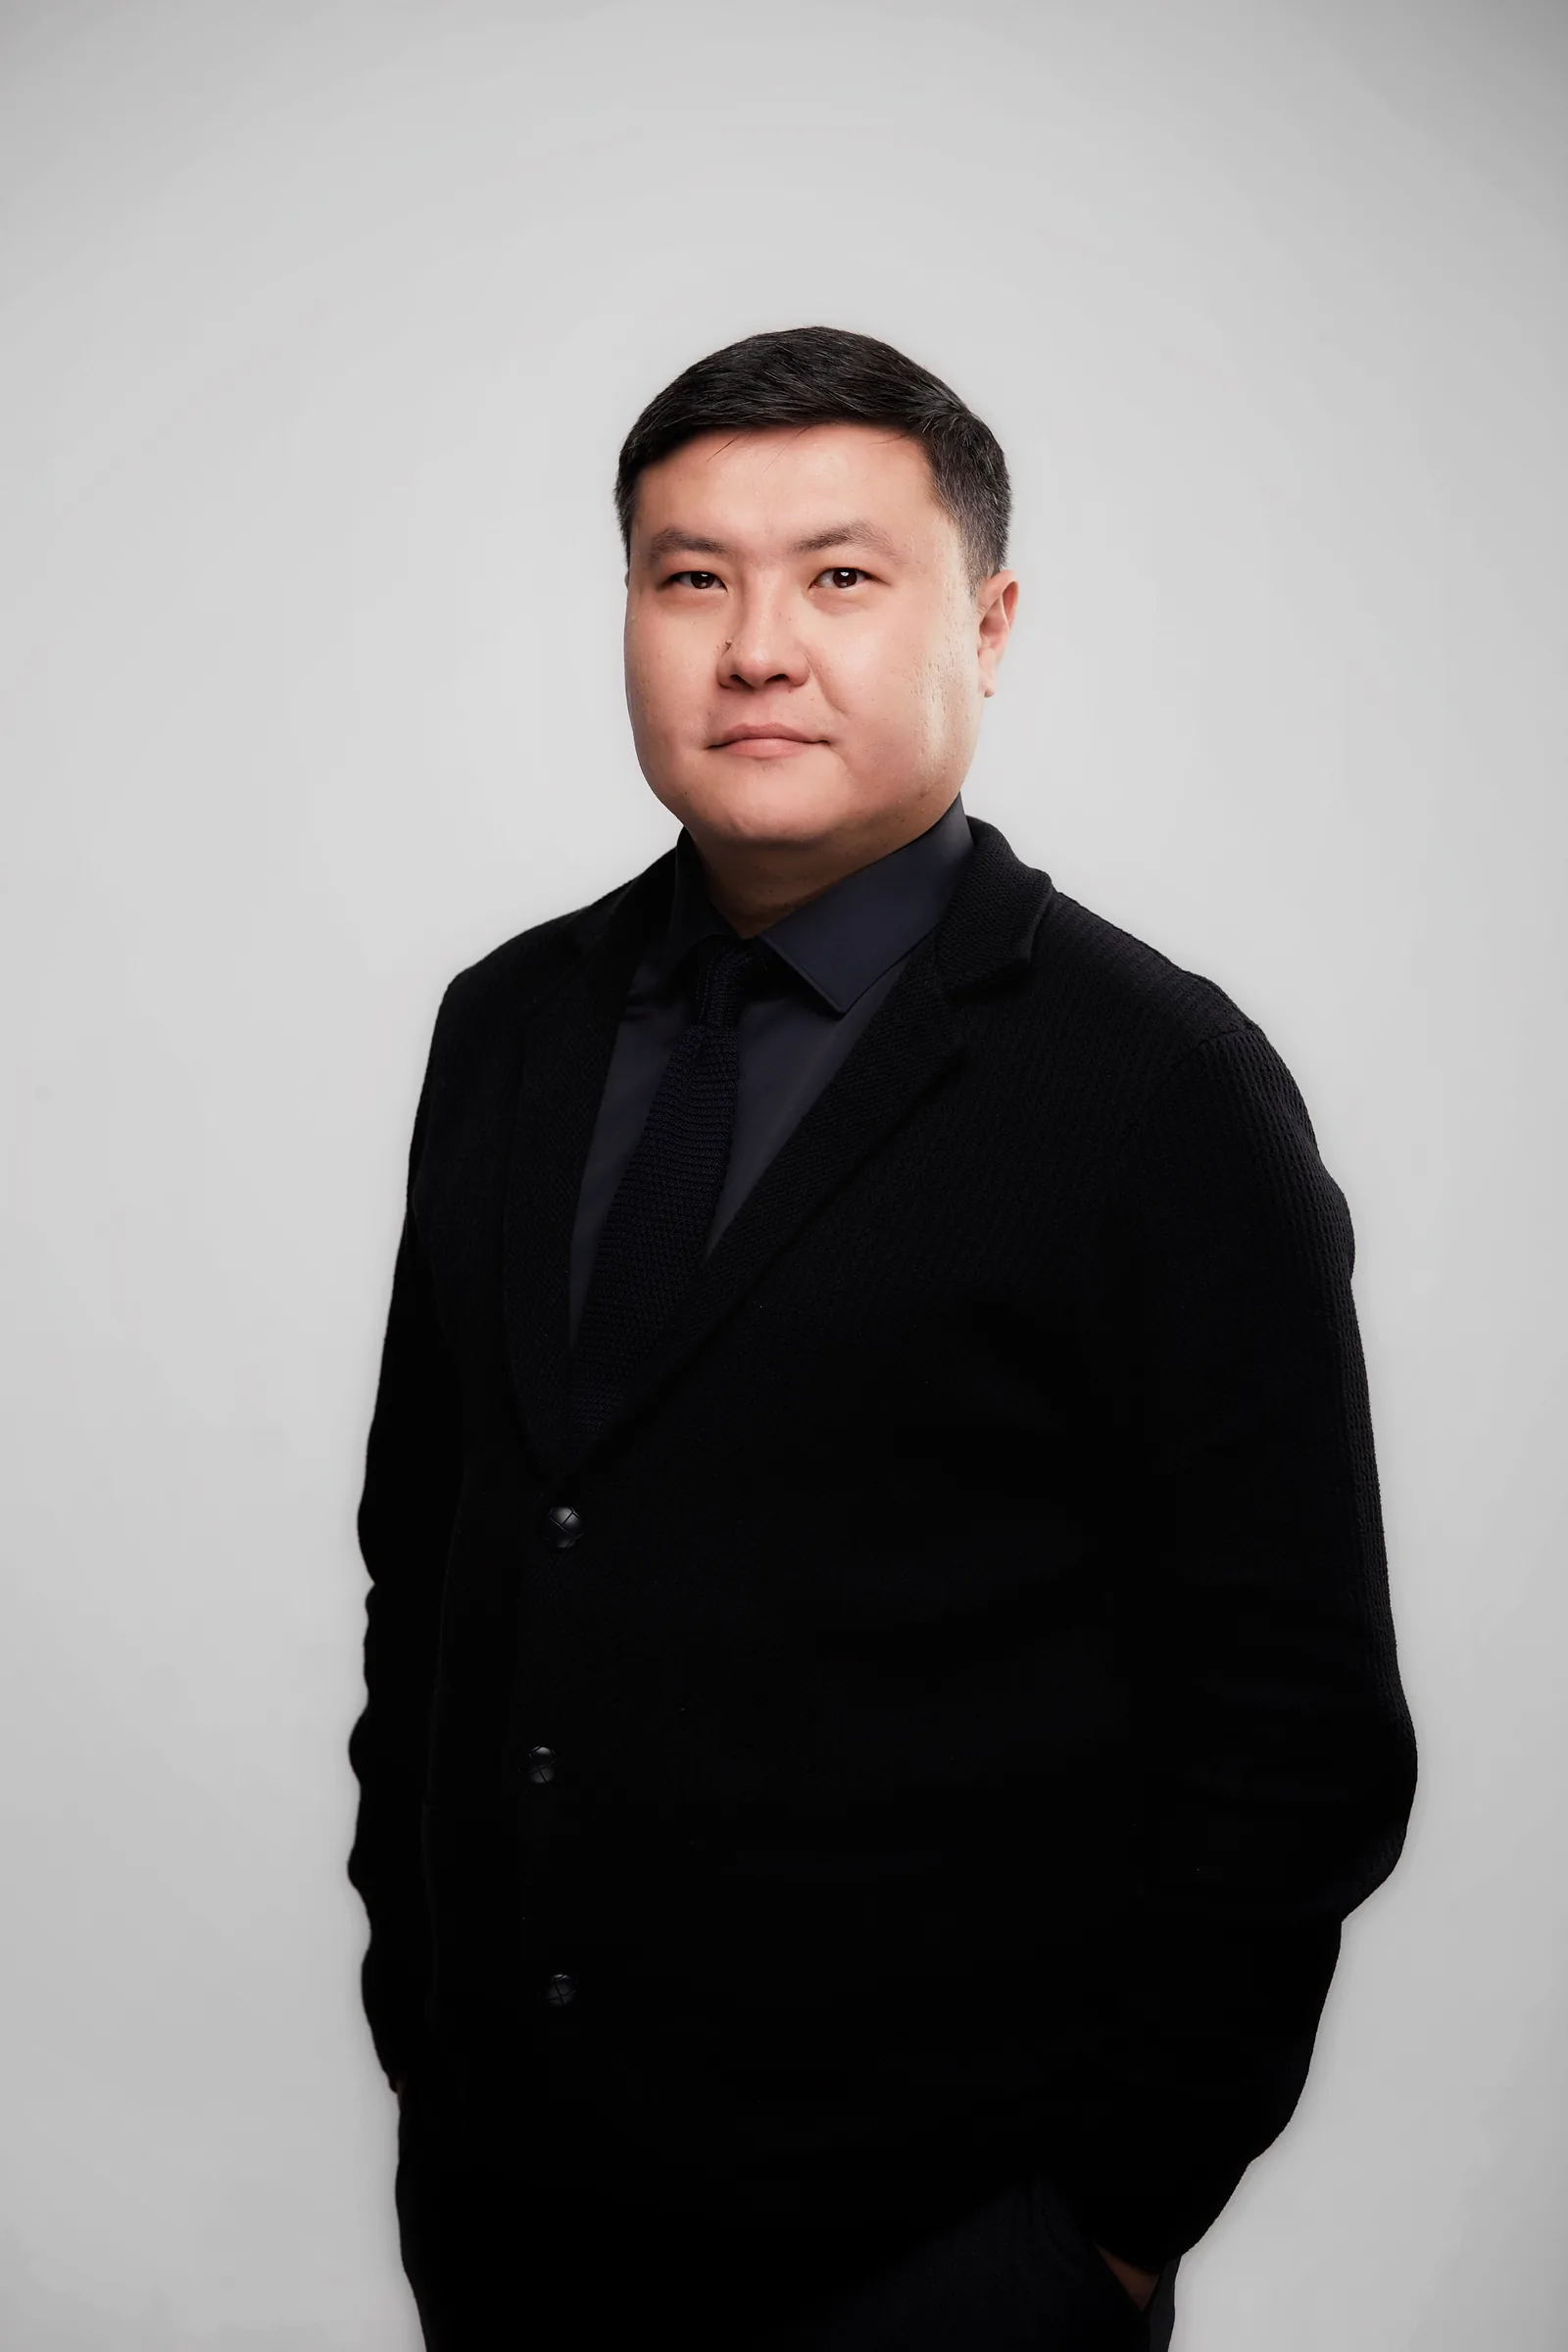
Alim Khamitov, venture capitalist, head of MOST Ventures funds
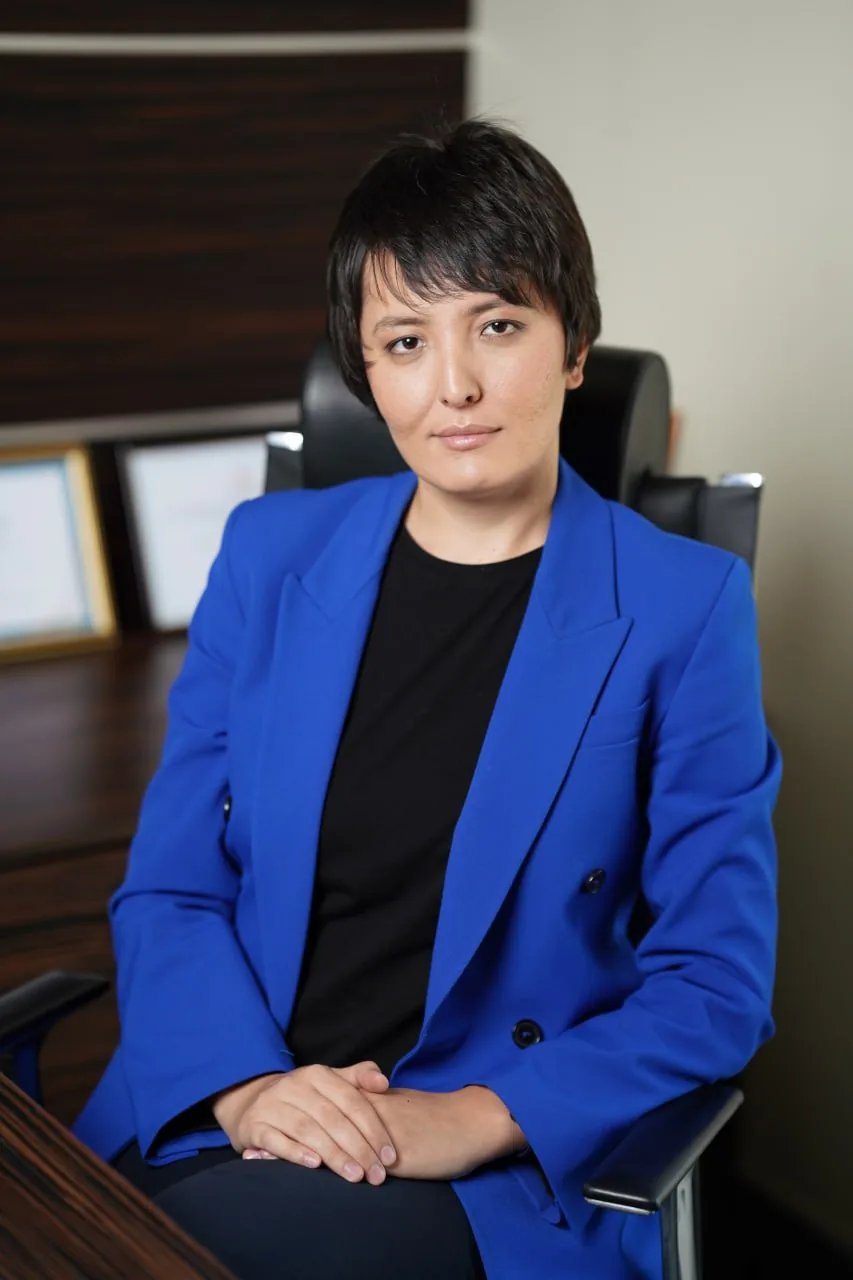
Evgeny Pitolin, co-chair of the Information Security Committee of the Qaztech Alliance
About themselves
Alim. I am a venture entrepreneur and investor. My main business is Most Holding, which I have been developing with partners for over 14 years, supporting technology entrepreneurs.
We have three venture funds for investments from Pre-Seed to Series A, as well as venture loans for IT companies. Additionally, we have opened two coworking spaces: Most Hub Almaty and Most Hub Tashkent.
We are developing the ecosystem: we host events, support startups, investors, and business angels. Recently, we organized the Central Eurasian Venture Forum and continue to develop the regional market.
Evgeny. I have been in IT and cybersecurity for nearly 25 years, and in recent years, I have focused on security awareness. In 2010-2012, we trained 5,000 Kazakhstani officials as part of a law enforcement project.
Currently, I receive three to five messages daily on Instagram with questions about personal cybersecurity—ranging from simple to complex—and I try to answer everyone. The state protects critical infrastructure, businesses protect their assets, but citizens are often left without support. It is important that someone thinks about them too.
What mistakes do founders make most often
Evgeny. One of the main problems with startups is that founders view the project as part of their personal life rather than as a business. This is evident even in spending habits: the choice between vacation and investing in marketing or cybersecurity is often made not in favor of the business.
The problem is that many people know little about digital security. If they do not pay attention to it in their personal lives, they also believe in business, especially at the start, that they can "deal with it later."
Founders think that hackers only target corporations, and their small startup is not interesting to anyone. This is a key mistake that puts both the business and customer data at risk.
Alim. In general, for most startups, information security is not considered a priority—it is a blind spot.
I communicate with founders daily; we review about 35 projects a day, and almost always hear: "Yes, security will be there, but not now." At the same time, there are real cases where companies lost everything in a day due to a lack of basic protection. And the founders did not even think that this could happen to them—right now.
The problem is solvable. Startups in the region are already thinking about scaling, investments, and products, but security is still not on the list of priorities. This is both a risk and an opportunity.
Information security is not just about passwords; it is also about protecting intellectual property, digital products, reputation, and user trust. It is important that this conversation has finally begun, and interest in the topic is growing.
Evgeny. Most startups start thinking about security only after an incident—sometimes it is difficult or too late to help. Here are the three most typical problems:
1. Risk of ignorance
Often, young teams use Western services for hosting, development, and data storage—unaware that this violates the law. Personal data of Kazakhstani users cannot be stored outside the country. This applies even if it is about marketing databases or HR data. If a startup grows, the first to arrive will not be an investor, but the regulator.
2. Risk of "speed" development
In the pursuit of a quick launch, startups sacrifice security for speed. By releasing releases and updates in a hurry, they get a vulnerable product where fixing errors later is more difficult and expensive.
3. Risk of integrations and open interfaces
Setting up integrations with partners via API is another risk. A partnership may end, but open interfaces may remain. Over time, control is lost, and access to data may be obtained by unauthorized persons.
These risks are especially relevant in the first years of a startup's life and require attention from the very beginning.
Examples of incidents that happened to young IT companies
Alim. Such cases happen both with us and abroad. One well-known case is the startup Cerebral in the mental health sector. The company collected customer data and shared it with advertising platforms, violating legislation. Despite having three million users and a valuation of over $4 billion, the data leak became one of the reasons why the startup did not go public. This problem could have been prevented in advance.
In Kazakhstan, a similar story happened with a FinTech startup: a database of clients with INNs was available in plain text via a link without protection. Anyone could access the data.
There are many such cases, but they are rarely discussed publicly. Perhaps it is worth collecting and discussing them openly—for example, in the format of streams—so that startups and investors can learn from others' mistakes.
Red flags in cybersecurity
Alim. As an investor, I often encounter typical problems in startups related to the lack of a security culture.
1. "We'll do it later." In 90% of cases, founders postpone security issues for the future. Often, there is no one responsible for this area in the team—neither internally nor on an outsourced basis.
2. Lack of role distribution. Instead of a structured system, everyone does everything. The CTO might be the only person with access to the entire system. His departure is a huge risk, especially if no one else understands the technical side.
3. Security of external integrations. Many startups use third-party platforms and APIs but do not always assess the risks of data transfer and legal consequences. The technical team should control this.
4. Lack of a security strategy in the roadmap. If a startup works with data, an information security strategy should be part of the roadmap. Sometimes we ask to conduct an external audit—this helps identify vulnerabilities in advance.
Conclusion: attention to security should be present even before problems arise. Conscious risk management, internal security culture, and documentation of processes are the foundation of any startup's resilience.
Alim. We have not had direct rejections specifically due to non-compliance with information security standards. We invest at early stages, and at this moment, strict security requirements are rarely imposed. But we always ask basic questions: how is the system architecture organized, where is the platform hosted, who has access, is encryption used, are confidential data processed.
In 2024, we invested in a security startup for the first time—ZenGuard AI, founded by guys from Kazakhstan who work in the US. This is an API platform for protecting generative AI services from prompt attacks, jailbreak scenarios, and data leaks. Currently, they already have more than 100 clients, and we believe in their potential.
We do not consider ourselves experts in the field of information security, but we understand that this market is growing. We are ready to support startups that create innovative and scalable solutions in this area.
About the popularity of startups in the field of information security
Alim. To be honest, out of 100 startups that come to us, only two or three work in the field of information security. This clearly reflects the situation in the market. I do not think that this sphere is underestimated—rather, there is currently a lack of expertise or understanding of real pain points.
Information security is definitely not considered a dominant direction among startups. We see projects in FinTech, EdTech, or HR much more often. Startups in the security field are rather the exception.
But currently, against the backdrop of rapid technological development and AI, more and more opportunities are appearing in this area. And, in my opinion, it is time to pay attention to it.
What founders most often ignore in terms of security
Evgeny. The problem is not only with the founders themselves. Many companies, especially fast-growing ones, completely forget about information security, focusing only on growth and profit. As a result, growth pains remain unresolved.
There are also investors who mindlessly buy up companies without checking their internal processes. Such holdings often look like a single corporation, but in reality, they are dozens of scattered businesses with their own teams and mistakes. No one builds a unified security system: "one-two—and into production." When the time comes to merge databases or launch joint projects, critical vulnerabilities surface.
Founders often ignore elementary things: common sense and a critical look. Many startups are created by very young people who do not take risks seriously. Even in our time, there are stories when founders transferred all the company's money to scammers.
Therefore, I always say: do not forget about natural intelligence. Use your head, do not be afraid to set rules and restrictions. If you do not do this—the market will. And then the cost of a mistake will be too high: loss of money, brand, and reputation.
Recommendations
Alim. I participate in several boards of directors and see that security issues are becoming more relevant. I would advise startups:
1. Find expertise outside. If there are no information security specialists in the team, attract experts.
2. Think about corporate governance. It is not necessary to create a board of directors immediately, but the presence of advisors helps to see weak spots and strategic risks. Sometimes an external view is enough to avoid critical errors.
3. Do not forget about intellectual property. This is also part of information security. Register IP rights not to specific individuals, but to the parent company, especially if you plan to enter international markets.
Evgeny. 1. Do not look for information security expertise within yourself. It is better to go to the market and attract the right people. I consult startups, but as a rule, it is free—startups simply do not have the budget. Nevertheless, helping and sharing knowledge is important and necessary. It is better to look for expertise outside—it is more reliable and effective.
2. Regularly test your infrastructure through Bug Bounty programs. This will help identify vulnerabilities in a timely manner. It is better to pay X to white hackers than 10X to real attackers later.
3. Delegate expertise in time and form a security culture within the team from the very beginning. Implement secure development and comply with personal data legislation.
Think about security in advance. Protect customer and employee data—it is an investment that will pay off.
The Tech on Telegram Follow The Tech on Telegram
Keep up with the latest technology and startup news.
Related reading


More from this author
News
zypl.ai begins operations in Japan and focuses on next-generation risk models
Mansur Ismagulov
News
Elon Musk's net worth has exceeded $700 billion for the first time
Mansur Ismagulov
Article Interviews
"Central Asian countries should build a joint ecosystem," — Bekhzod Ismoilov on the development of AI in the region
Mansur Ismagulov
Article Interviews
Bloom's Taxonomy and Engineering Levels: A Practical Growth Model
Mansur Ismagulov
Article Useful
How the IT industry in Azerbaijan developed in 2025: key events
Mansur Ismagulov
News
Tajikistan has become a new member of the regional innovation alliance Central Asian Innovation Hubs.
Mansur Ismagulov