The Evolution of Cyber Threats: Why Security Systems Must Be Adaptive
Author - Mansur Ismagulov
The Tech AI
Get the key points in seconds - a short summary from The Tech AI.
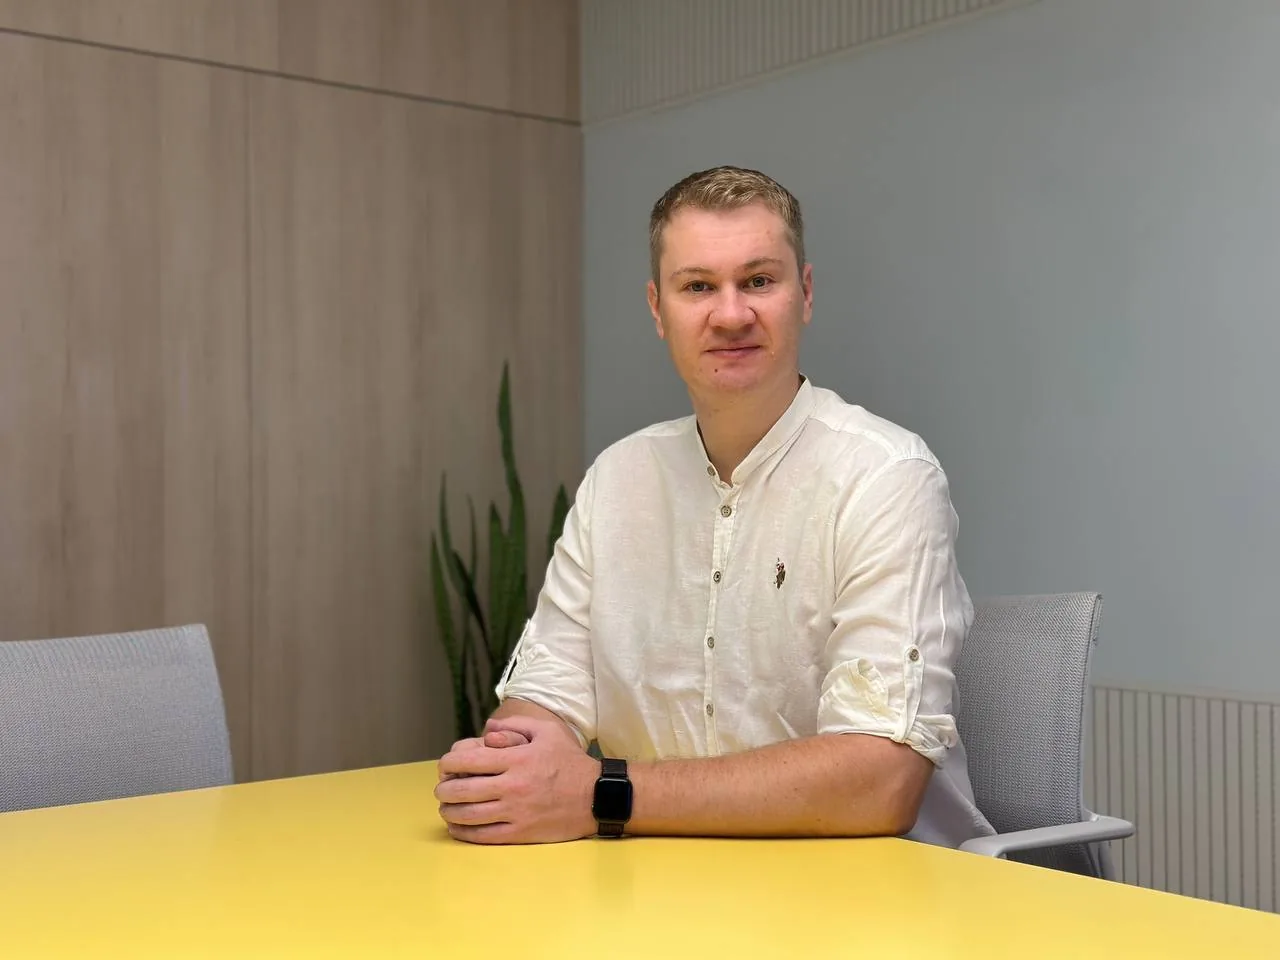
Artem Frolov, Cyber Security Engineer/Architect, highlights the rise of targeted APT attacks, which require adaptive defense strategies. Traditional methods are no longer effective against threats involving long-term reconnaissance and social engineering. To counter these threats, comprehensive measures are necessary: employee training, regular audits (pentesting), real-time monitoring, and backup systems.
Artem Florov, Cyber Security Engineer/Architect
In recent years, the nature of cyber threats has changed beyond recognition. If companies used to mainly face random attacks based on the exploitation of known vulnerabilities, today we are witnessing an explosive growth in targeted attacks known as APT or Advanced Persistent Threat. These are attacks that cannot be described as chaotic or random. Behind each of them lies a carefully thought-out strategy, years of experience, and the resources of entire organizations aimed at a specific victim.
Why is this important? Because traditional security approaches that worked five to ten years ago are no longer coping with such threats. Simply updating systems and installing antivirus software will no longer protect a company. We are dealing with threats that adapt to your defenses, study your infrastructure, and find weak spots. This is no longer a question of "if an attack will happen," but rather "when it will happen."
Throughout my career, I have seen how the evolution of cyber threats forces companies to completely change their security strategies. From working with industrial systems, where perimeter protection was a key element, to protecting global web platforms, where the reputation and data of millions of users are at risk every minute, I have observed one important trend: flexibility and the ability to adapt to new challenges have become decisive factors in successful protection.
More than ten years ago, it became obvious to me that perimeter protection alone was not enough. It was necessary to implement approaches that allow detecting attacks within the network using Network Traffic Analysis (NTA). This became an important step in building comprehensive strategies that not only prevent external threats but also respond promptly to hidden attacks that have already penetrated the infrastructure. This approach has become an integral part of modern security systems.
APT attacks, like other modern threats, are not just a technical challenge. They are a challenge to the entire system: people, processes, and technologies. This evolution requires us not only new tools but also a new approach — systemic, adaptive, and proactive. And this is exactly what I want to talk about in this article.
The Difference Between Random Attacks and APT
Not all cyberattacks are the same. Understanding the difference between random attacks and targeted APT threats helps in better assessing risks and choosing the right protection strategies.
Random attacks are usually based on the exploitation of widely known vulnerabilities and weaknesses in systems. Such attacks are not aimed at a specific company — attackers simply look for any target that turns out to be vulnerable.
For example, if your infrastructure uses a public service with a software version containing a known vulnerability, an attacker may try to exploit it. Once inside the outer perimeter of the system, the attacker will strive to establish a foothold and expand access to obtain as much data as possible or use your company's resources for further attacks.
Targeted attacks or Advanced Persistent Threats differ fundamentally. Here we are talking about the actions of experienced groups that choose their target in advance and prepare carefully for the attack. Their victims are most often large organizations whose data have high financial, strategic, or intellectual value.
Features of APT attacks:
- Careful reconnaissance: attackers use OSINT methods — collecting data from open sources, researching the company's infrastructure, its employees, and counterparties.
- Personalization of attacks: phishing, fake requests from "partners," fake pages, and other methods aimed at specific employees are used.
- Duration: an APT attack can last for months, and sometimes years, until the attackers achieve their goals.
- Damage: such attacks cause not only financial damage but also undermine the company's reputation, which is especially critical for major players.
Understanding the difference between random attacks and APT allows for correct prioritization in protection. If random attacks can be prevented using standard measures such as regular updates and basic security settings, then APT requires a more comprehensive approach: from deep monitoring to integrating protection with business processes.
APT attacks are a challenge that cannot be ignored, as the consequences in case of success can be catastrophic for the company.
Tactics and Techniques of APT Attacks
Targeted attacks are characterized by a high degree of preparation and complexity of implementation. Attackers use a wide arsenal of tactics to achieve their goal. Below I will tell you about the key methods used in such attacks.
Phishing and Social Engineering
The first step of any APT attack is gathering information about the employees of the victim company. Using OSINT — Open Source Intelligence methods, attackers find publicly available data about employees, their contacts, and positions. Leaked databases and social networks become valuable tools for them.
Today, phishing has gone beyond traditional email campaigns. Attackers adapt by sending malicious links via SMS, messengers: WhatsApp, Telegram, personal email accounts. This makes attacks more personalized and difficult to detect. The main goal is to deceive the victim and force them to disclose data or download malware.
Attacks on Counterparties
Often, attackers do not attack the company itself, but its partners or suppliers. Companies in the supply chain may have weaker protection, making them a convenient entry point. Having penetrated the counterparty's infrastructure, hackers use trusted connections to penetrate the target company without hindrance.
Activity on the Outer Perimeter
Along with social methods of attack, attackers conduct active actions on the company's perimeter:
- Vulnerability scanning: searching for weak spots in publicly available services.
- DDoS attacks: sometimes used as a diversion to hide more targeted actions. For example, an attack may distract security specialists while hackers exploit vulnerabilities.
Gathering Information About Systems
To prepare as much as possible, attackers study what technologies and systems are used in the organization. For this, they may use:
- Fake surveys: posing as representatives of vendors or research companies, they try to obtain data about system configurations.
- Fake accounts: fake profiles are created that mimic solution providers to gain trust and request technical information.
Development of Targeted Exploits
Based on the collected information, attackers develop individual attack tools that take into account the features of the company's infrastructure. One of the most famous examples is Stuxnet, a virus specifically created to attack industrial systems. Such exploits are difficult to detect because they are unique and targeted at specific goals.
Why Security Systems Must Be Adaptive
In the world of cybersecurity, one of the biggest mistakes is believing that threats can be predicted and completely neutralized in advance. Modern attacks, especially targeted ones — APT, are becoming increasingly complex, personalized, and technologically advanced. This is why adaptability is not just a trend, but a necessity for resilient protection. Just yesterday, the main risks came from email phishing and vulnerabilities in public services, and today attackers use messengers, fake applications, and even specially created exploits. Every new technology or process — from remote work to IoT — opens up new attack vectors.
For example, APT attacks adapt to protection: if a company has strengthened its perimeter, attackers switch to suppliers. If you have increased employee awareness, hackers use technical vulnerabilities or develop targeted exploits.
Today, it is impossible to create a universal system that can withstand all possible attack scenarios. This is due to two main reasons:
- Complexity of the ecosystem: modern companies have many integrations, partners, suppliers, and digital channels, each of which can become an entry point for attackers.
- Level of attacker preparation: APT groups use tactics that were previously unseen, develop new hacking methods, and find ways to bypass existing defenses.
An example is a supply chain attack, where attackers use trusted relationships between companies to penetrate the target infrastructure.
Practical Measures for Adapting to Modern Threats
1. Employee Training: Security Awareness
The strongest company protection can become useless if employees are not aware of basic digital hygiene principles. Attackers actively use social engineering methods, which means employee training is the first and most important level of protection.
- What Security Awareness programs include:
— recognizing phishing and suspicious links
— training on using strong passwords and their secure storage
— creating a culture of awareness about cyber threats.
- Regularity: We have implemented mandatory training for all company employees with program updates every six months to account for new attack vectors.
2. Regular IT Security Audit: Pentest
Constant penetration testing — pentest — allows identifying vulnerabilities before attackers can exploit them.
- Benefits of pentest:
— testing under real attack scenarios
— assessing resilience to the latest hacking techniques.
- Results: We included audit results in the improvement plan, which significantly reduced the risk of exploitation.
3. Effectiveness of Used Solutions
The world of cybersecurity is changing, and tools that worked well a year ago may become outdated. Constant evaluation of used solutions is the key to keeping protection relevant.
- What is evaluated:
— compatibility of tools with the company's current needs
— scalability and ease of use
— effectiveness in detecting and preventing real threats.
- How we do it: we regularly conduct internal audits and involve independent experts for evaluation.
4. Backup
Backup remains one of the most underestimated protection measures. However, in the face of growing ransomware attacks, it becomes critically important.
- Recommendations:
— copying critical data to isolated storage media
— regular testing of data recovery
— storing backups in offline mode for additional protection.
5. Real-Time Monitoring
Monitoring systems are the eyes and ears of security. They allow tracking events, system behavior, and identifying anomalies in real time.
- What monitoring systems include:
— log and behavior analysis
— setting up alerts for critical events
— automation of data correlation using SIEM.
6. Incident Response Plan
When an incident occurs, the team should not have time to hesitate. A clear action plan allows minimizing damage.
- Plan elements:
— response scenarios for various types of threats
— role distribution within the team
— regular drills and plan testing.
Each of the listed measures is part of an adaptive approach to security. Only by combining training, technology, and clearly structured processes can we counter modern threats.
Continuous development of the security system is a necessity. Effective protection is not only about technology but also about training people, regular process audits, and the ability to learn from every incident.
By investing in employee training, technology updates, and deep threat analysis, companies lay the foundation for sustainable growth. Every threat is a challenge, but also a chance to rethink approaches, improve processes, and make your positions even stronger.
My advice is simple: start small, but act systematically. Security is a continuous process. Build a system that will not only protect but also evolve with you. After all, success in cybersecurity is success in business.
Author: Artem Frolov
The Tech on Telegram Follow The Tech on Telegram
Keep up with the latest technology and startup news.
Related reading







More from this author
News
zypl.ai begins operations in Japan and focuses on next-generation risk models
Mansur Ismagulov
News
Elon Musk's net worth has exceeded $700 billion for the first time
Mansur Ismagulov
Article Interviews
"Central Asian countries should build a joint ecosystem," — Bekhzod Ismoilov on the development of AI in the region
Mansur Ismagulov
Article Interviews
Bloom's Taxonomy and Engineering Levels: A Practical Growth Model
Mansur Ismagulov
Article Useful
How the IT industry in Azerbaijan developed in 2025: key events
Mansur Ismagulov
News
Tajikistan has become a new member of the regional innovation alliance Central Asian Innovation Hubs.
Mansur Ismagulov