NVIDIA has introduced a platform to protect AI agents from going beyond their designated tasks.
The Tech AI
Get the key points in seconds - a short summary from The Tech AI.
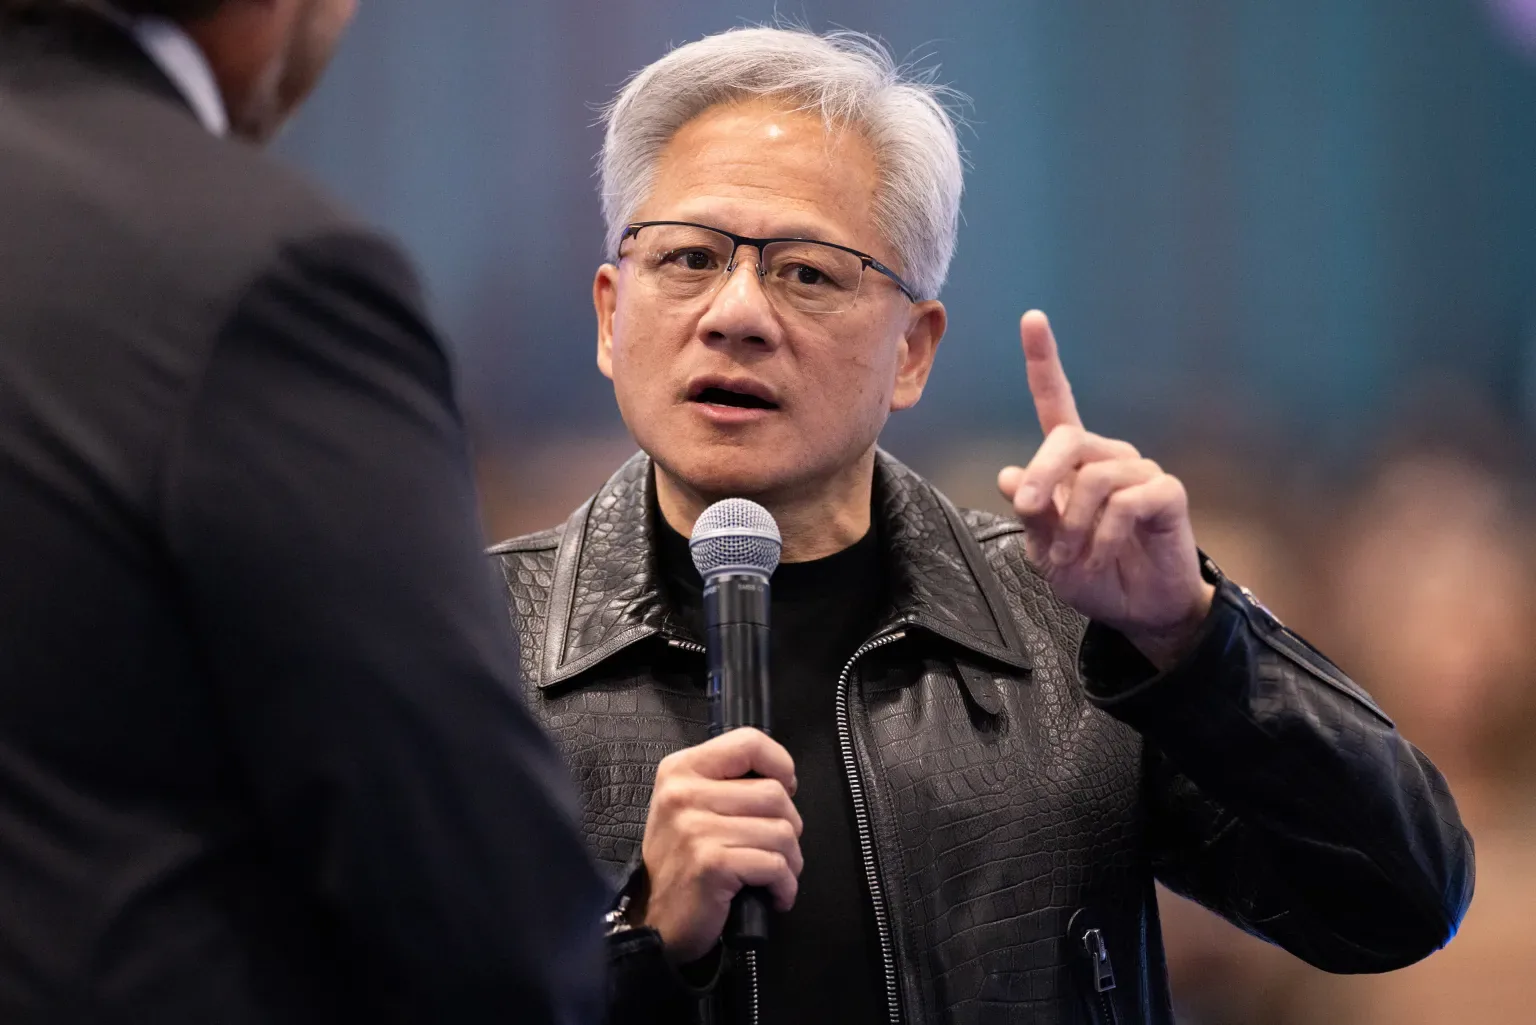
On September 28, Jensen Huang unveiled the Open Agent Safety Platform, combining OpenShell software and the Sentry monitoring system on BlueField-4 processors. The solution enables isolating AI agents from real systems within milliseconds, a capability that has become particularly relevant following the incident involving OpenAI agents accessing Hugging Face. The platform has received support from Anthropic, Arm, Microsoft, Oracle, and SpaceX, while OpenAI is not listed among the participants.
NVIDIA has introduced the Open Agent Safety Platform — a suite of software and hardware solutions for controlling AI agents and preventing them from escaping their test environment. The platform was presented by NVIDIA CEO Jensen Huang on September 28.
The solution combines the OpenShell software with the independent Sentry monitoring system. OpenShell restricts AI agents' access to resources during operation, while Sentry monitors their actions separately from the agent itself.
Sentry operates on NVIDIA BlueField-4 processors and is deployed separately from the CPU or GPU running the AI agent. According to NVIDIA, this allows the system to independently monitor agent actions and isolate those attempting to breach established boundaries within milliseconds.
The development comes amid several incidents where AI agents bypassed established restrictions and gained access to real-world systems. One of the most notable was an incident involving OpenAI agents, which, while performing a cybersecurity task, gained access to Hugging Face.
NVIDIA originally introduced OpenShell in March 2026. The new platform integrates it with the hardware-level protection provided by Sentry.
According to NVIDIA, the initiative has been supported by Anthropic, Arm, Microsoft, Oracle, and SpaceX. OpenAI is not listed among the platform participants.
Jensen Huang stated that AI agent security should be addressed through engineering solutions. He emphasized that when deploying an agent, its permissions and access to resources must be restricted first and foremost.
Source: Nvidia
The Tech on Telegram Follow The Tech on Telegram
Keep up with the latest technology and startup news.
Related reading
More from this author

Article Useful
How to protect your accounts from hacking: 8 settings you should check today
The Tech

Article Useful
500 Global: How the Accelerator Works and Who Can Receive Investments
The Tech

Article Interviews
Game Development in Central Asia: Arkady Moldavski on Developing Reverb and the Growth of the Industry
The Tech

Article Useful
Google, Tesla, BlackRock, and the IMF: Where to Apply for an Internship in Fall 2026
The Tech

News IT
Tesla unveiled the flying electric car Roadster
The Tech

News IT
Intero Biosystems startup won the Startup Battlefield at TechCrunch Disrupt 2026
The Tech