Meredith Whittaker — on why it is dangerous to trust AI chatbots
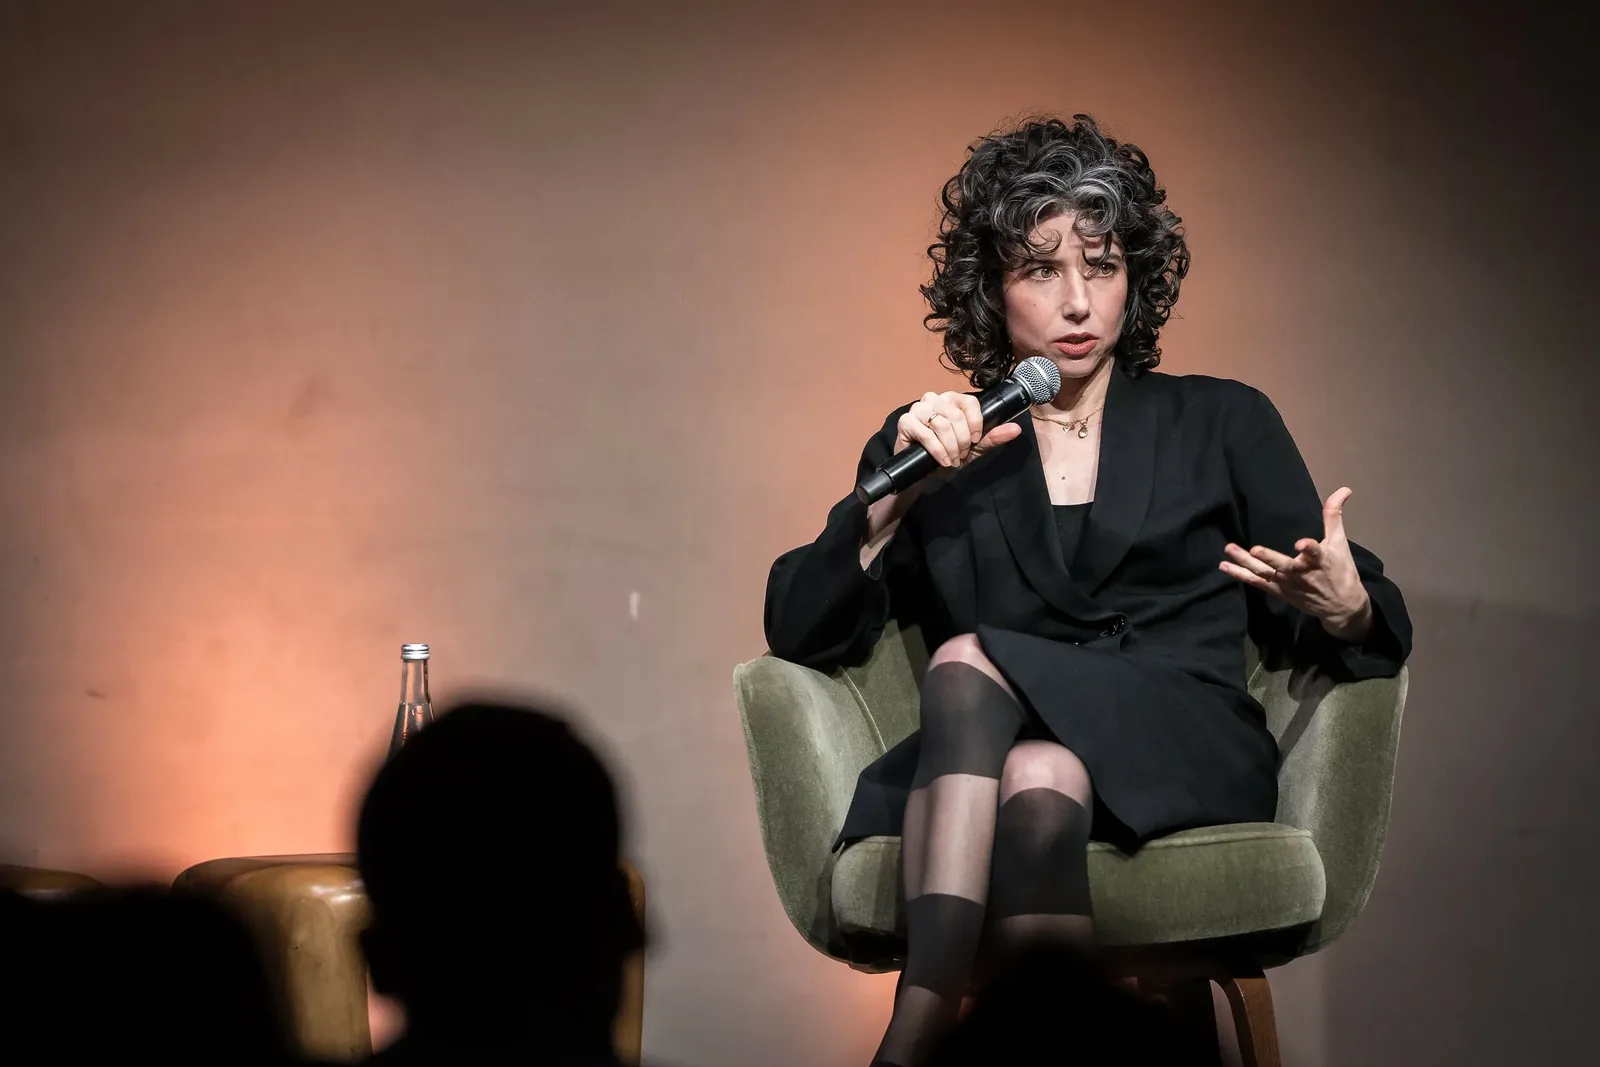
Meredith Whittaker, who leads Signal, gave an interview to journalist Mishal Husain, in which she explained why agentic AI is structurally incompatible with privacy — and why users who trust chatbots with their personal thoughts are making a mistake.
AI is not a conversational partner
Whittaker warned that AI chatbots are not friends, conscious beings, or full-fledged conversational partners. According to her, she uses AI only for formatting documents but does not ask it questions. She takes her thinking and writing seriously and does not want the process of refining an idea to be blocked or displaced by a system response that merely averages existing content.
Whittaker warns: systems are designed to simulate empathy and understanding, but at their core lies pattern matching from training data, not genuine comprehension. Trusting them with personal matters means voluntarily handing over personal information to systems with opaque data handling practices.
When an assistant becomes surveillance
The harshest criticism is directed at Mustafa Suleyman, CEO of Microsoft AI, who predicted that users would be able to entrust Copilot with Christmas shopping—for this, the agent would “eavesdrop” on family group chats to figure out what everyone wants.
Whittaker methodically listed the access such a system would require: credit card, browser, Signal, the ability to send messages on behalf of the user, home address, calendar.
According to Whittaker, such a system gains too broad access to numerous applications and services. In the case of Signal, this is equivalent to a backdoor—a hidden entry point that bypasses all security measures to access data.
Agentic AI kills encryption
The core of Whittaker’s argument is that agentic AI systems, which require nearly full access to a user’s digital life to operate, are structurally incompatible with end-to-end encryption. An agent capable of reading messages before encryption or after decryption renders encryption meaningless from a privacy perspective.
This is why, in January 2026, at Davos, Whittaker called agentic AI “dangerous” for secure applications, and in an essay for The Economist, she accused operating system manufacturers of “hollowing out” Signal’s ability to guarantee privacy by embedding agents into their platforms.
Three companies decide for everyone
Microsoft is building an operating system around agentic computing—Project Solara, presented at Build 2026, replaces traditional applications with AI agents as the primary interface. Similar strategies are being implemented by Google, Apple, and OpenAI.
Whittaker warns: in the world, control is held by just three companies—Google with Android, Microsoft with Windows, and Apple with iOS. According to Whittaker, these three companies can unilaterally make decisions that fundamentally undermine collective cybersecurity.
This architectural shift creates databases of users’ entire digital lives, which become the primary target for both hackers and governments.
Convenience or privacy
Whittaker’s position diverges from the dominant Silicon Valley narrative, where an agentic future is portrayed as an inevitability that boosts productivity.
Her counterargument: the productivity gains achieved at the cost of handing over control over messages, calendars, contacts, and financial information to corporate AI are not gains at all, but a trade-off in which users exchange privacy for convenience without understanding its terms.
The Tech on Telegram Follow The Tech on Telegram
Keep up with the latest technology and startup news.
Related reading




More from this author

Article Useful
How to protect your accounts from hacking: 8 settings you should check today
The Tech

Article Useful
500 Global: How the Accelerator Works and Who Can Receive Investments
The Tech

Article Interviews
Game Development in Central Asia: Arkady Moldavski on Developing Reverb and the Growth of the Industry
The Tech

Article Useful
Google, Tesla, BlackRock, and the IMF: Where to Apply for an Internship in Fall 2026
The Tech

News IT
Tesla unveiled the flying electric car Roadster
The Tech

News IT
Intero Biosystems startup won the Startup Battlefield at TechCrunch Disrupt 2026
The Tech